OpenAI and Poland’s NASK are partnering on AI safety, security, and technical research to strengthen safeguards and support a more resilient digital ecosystem.
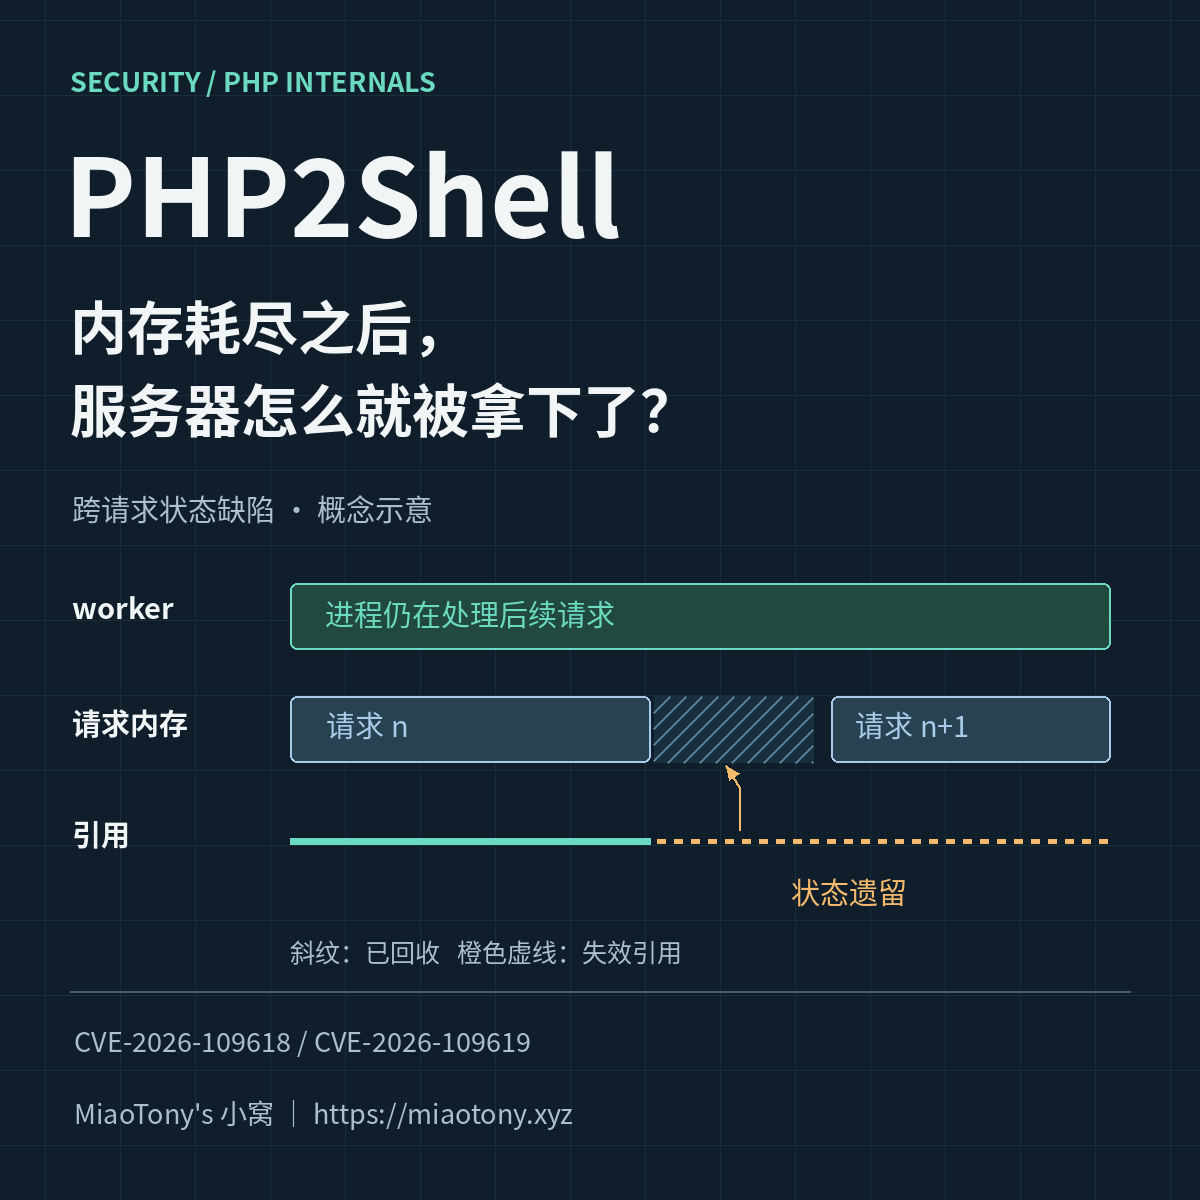
本文分析PHP漏洞CVE-2026-109618与CVE-2026-109619,结合官方公告、补丁源码和公开利用,拆解三条利用路径、可复用攻击原语及完整武器化链路,并讨论修复与检测方法。
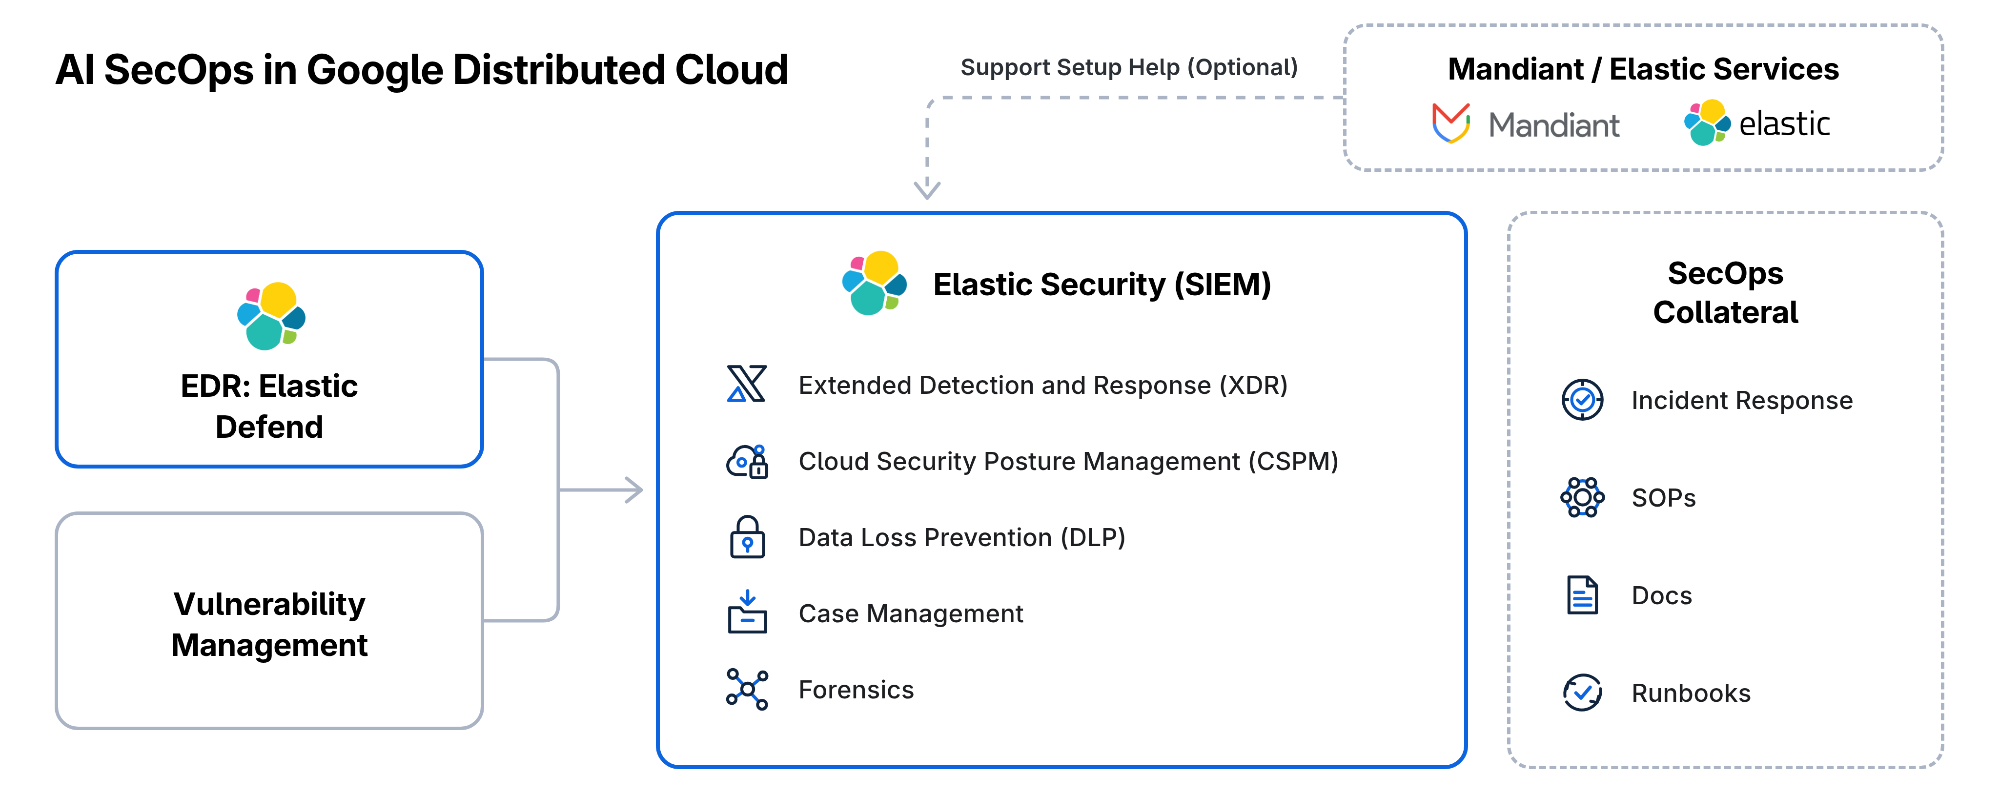
Elastic Security 与 Google Distributed Cloud 气隙环境集成,将 SIEM v2 和 EDR v2 嵌入平台,提供统一安全运营。该方案整合 SIEM、EDR、威胁情报和 SecOps 基础,帮助主权及受监管客户在完全断网环境中实现自动化防御,缩小攻击速度差,降低运维负担。
Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so the upgrade is a version bump. This server-side guide covers enabling DPoP and RFC 8693 Token...
Block is building AI-powered security with OpenAI. Its security team investigates threats faster and proposes patches in minutes.
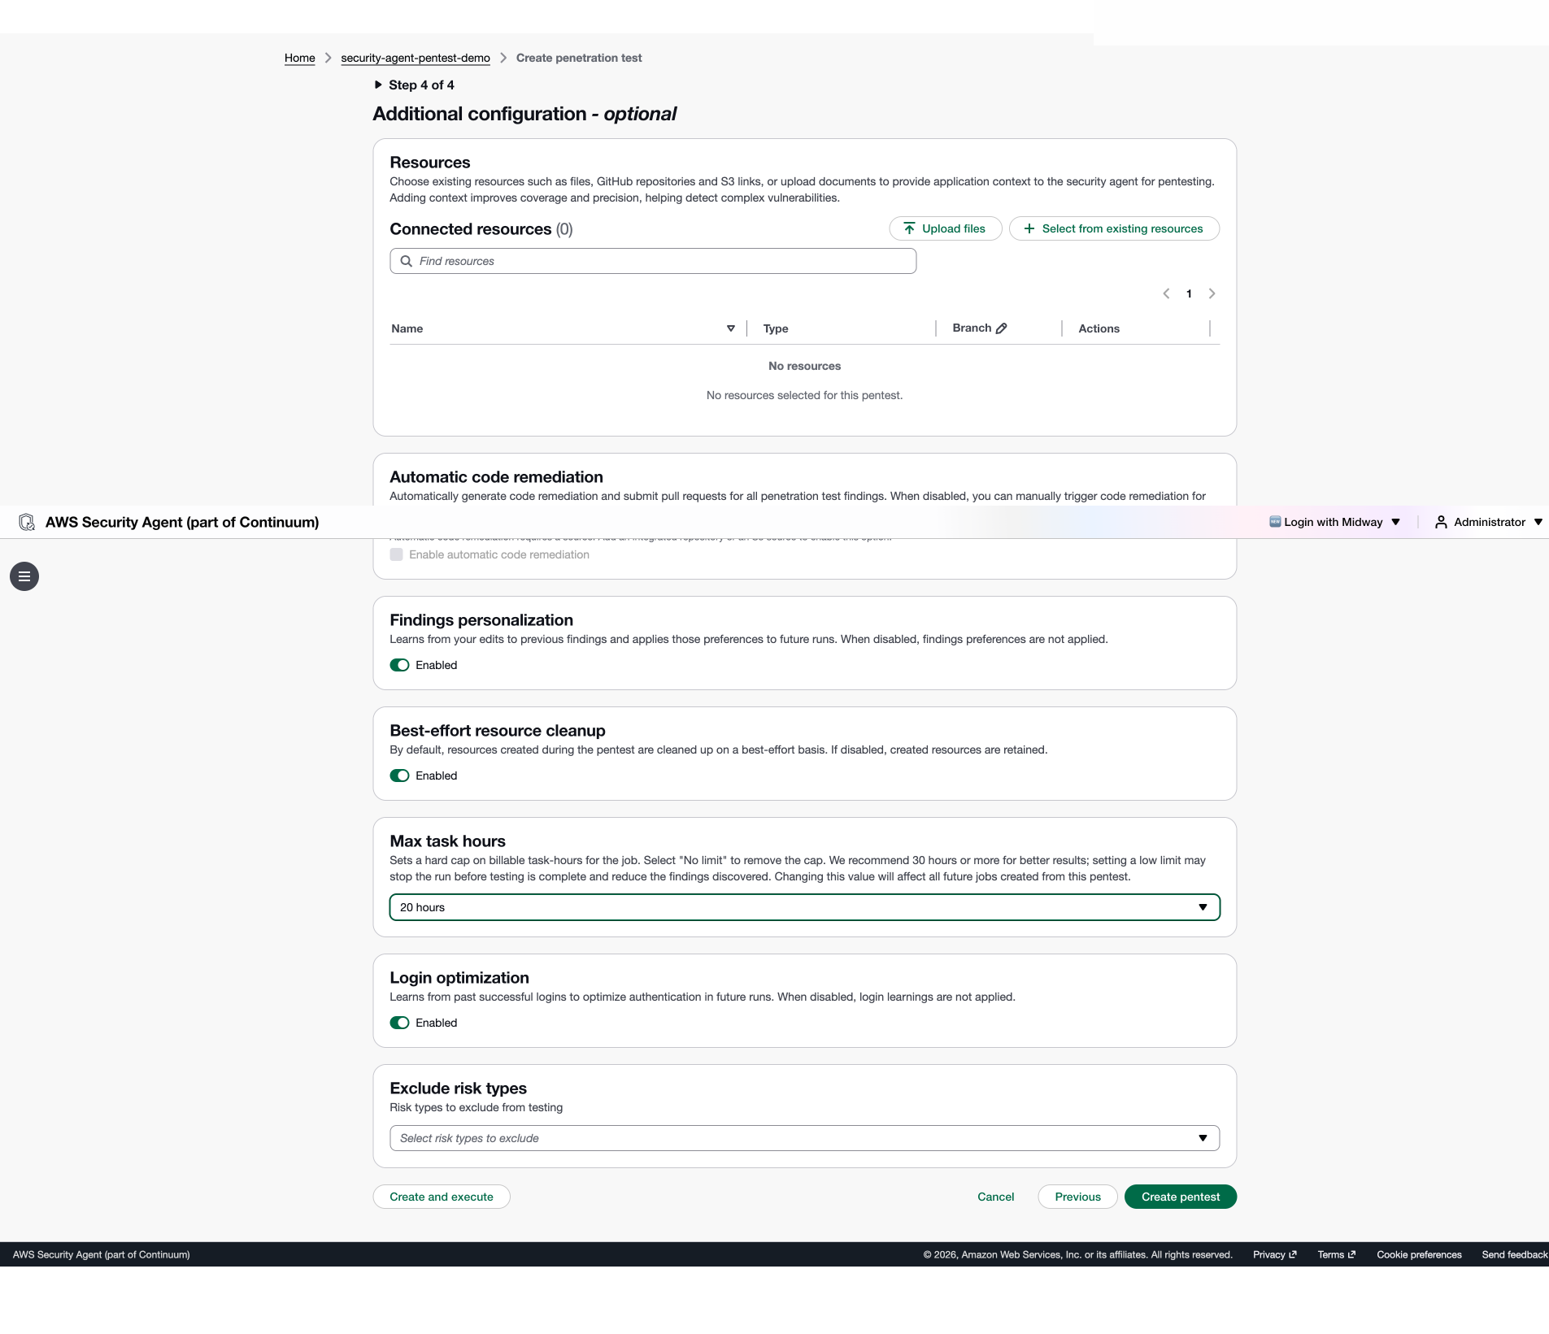
Jean Lilly为B2B珠宝店铺提供3D设计平台,研发团队二十多人但无专职安全工程师。传统外部渗透测试需2~4周、费用5~15万元,难以跟上发布节奏。采用AWS Security Agent后,开发团队可按需发起测试,将验证缩短至数小时,并通过授权、范围、凭据和成本上限的可重复流程,优先修复有证据的高危漏洞。
基于 PostgreSQL 17.11 实测,分析“new row violates row-level security policy”错误:该错误有四种形式、六类成因,包括租户不匹配、未设置租户、缺少插入策略、RETURNING 或 ON CONFLICT 需要 SELECT 策略、限制性策略拒绝、upsert 命中无权更新的行。排查时应检查当前租户设置、pg_policies 中对应命令与角色的策略,以及语句是否读取该行。
Every October, Cybersecurity Awareness Month reminds us the importance of protecting our digital lives. The theme for 2026 is ‘Don’t Make It Easy for Them,’ with the National Cybersecurity...
Elastic加入OpenAI Daybreak防御网络,将GPT Cyber模型引入Elastic Security,通过托管推理服务提供告警研判、调查与修复能力。OpenAI承诺投入10亿美元补贴公共机构,并与MS-ISAC试点保护水务等关键基础设施。该方案帮助政府、国防、教育等资源有限部门应对AI驱动的快速攻击,无需新建AI基础设施,且支持政府自管或隔离环境中的模型。
Google's AndroidX Security State libraries enables apps to verify security patch status at the individual component level, rather than relying on a single, device-wide security patch date. By...
Archestra released OpenAPPA, an open-source security engine designed to stop data exfiltration caused by prompt injection or model hallucination. The team reports zero successful attacks when...
A recent article by Anil Madhavapeddy argues that AI agents can turn publicly available clues about software vulnerabilities into working exploits, reducing the effectiveness of traditional...
Envoy Gateway has released v1.9.1, a maintenance release that focuses heavily on security, upgrade reliability, and operational correctness following the broader v1.9 release. By Craig Risi
A look at two InfoQ online certification cohorts covering security and privacy decisions in production AI systems and the verification needed when coding agents work in existing codebases. By...
There was a flurry of activity during the week of September 21st, 2026, highlighting: second milestone releases of: Spring Boot, Spring Batch, Spring Security, Spring AMQP, Spring Integration,...
While there is no single prescription for energy security, strengthening “response capacity,” such as by establishing stockpiles, substituting sources, and diversifying suppliers, is essential....
GitHub Copilot 重构差异界面,可流畅打开百万行代码的拉取请求及数百条行内评论;并将 Copilot 代理运行时迁移至 Rust,重写 80 万行生产级代码,此前因成本过高难以实现。
Security researcher Patrick Wardle revealed an unpatched zero-day vulnerability in Meta's Muse desktop client for macOS. This flaw lets unprivileged software manipulate the assistant's extensive...
该文本仅为 Tanzu Spring 的订阅推广信息,无实质文章内容可总结。
OpenAI CEO Sam Altman discusses AI safety, human control, and international cooperation in remarks to the United Nations Security Council.
完成下面两步后,将自动完成登录并继续当前操作。